- MFA
- on every account we manage
- 0
- shared passwords: 1Password with an audit trail
- 1
- incident plan, written before one happens
- 24/7
- a person answers when something looks wrong
What is included.
What ALCO does for you under security, in plain terms.
Assessment against a framework
We measure what you have against a named control set, NIST CSF, CIS, HIPAA Security Rule or PCI DSS, and hand you findings in order of risk with the business impact spelled out.
MFA everywhere
Multi-factor on email, remote access, admin accounts, banking and the line-of-business apps that support it. Legacy sign-in methods turned off.
Hardening
Endpoints, servers, identity and cloud tenants brought to a documented baseline, with exceptions recorded rather than forgotten.
Passwords done properly
1Password for the whole company: shared vaults, no spreadsheet, an audit trail, and offboarding that actually removes access.
Phishing training that sticks
Short awareness training plus realistic simulated phishing. People who click get a gentle lesson, not a telling-off, and the click rate falls.
Written policies
Acceptable use, access control, incident response, backup, vendor and remote work policies written for your business and short enough to be read.
Incident response, in advance
Who to call, what to isolate, who talks to customers and the insurer, written down and walked through before anything happens.
Questionnaires and insurance
Cyber insurance applications and customer security questionnaires answered with evidence, not optimism. Where the honest answer is no, we give you the plan to make it yes.
Readiness for HIPAA, PCI DSS, SOC 2, CMMC
The control matrix, gap list, remediation and evidence set that an assessor expects. We prepare you; the independent assessor or auditor makes the formal call.
How it works.
Four steps, each one written down as we go.
- 1
Scope and assess
We agree the systems, data and framework, then inspect configuration and evidence rather than sending a questionnaire and believing the answers.
- 2
Fix by risk
Identity and exposed paths first, hygiene after. Each fix is logged in myALCO so you can show when it happened.
- 3
Train and document
Policies approved, staff trained, phishing simulations started, incident plan rehearsed.
- 4
Review and keep evidence
Quarterly review of findings, click rates, new risks and policy changes, with the evidence filed as you go.
Who this is for.
Clinics, practices and anyone holding PHI
HIPAA wants documented, risk-based controls. This builds them and the paperwork that proves it.
Businesses taking cards or serving bigger customers
PCI DSS self-assessments and enterprise security questionnaires stop being a scramble.
Anyone renewing cyber insurance
The form asks about MFA, backups, EDR and training. We make every answer true before you sign it.


Questions people ask.
Will this make us HIPAA or PCI certified?
There is no HIPAA certification, and PCI DSS and SOC 2 are attested by qualified independent assessors. ALCO gets you ready and keeps the evidence; the assessor or auditor makes the formal decision. We will never tell you otherwise.
We are small. Do we really need this?
Small businesses are the usual target because the controls are usually missing. The core set, MFA, backups, patched devices, trained people and a password manager, is affordable and most of this page is about doing those well.
Do you do the phishing simulations yourselves?
Yes, as part of the service. The emails look like the real thing, the lesson for anyone who clicks is short and kind, and you see the trend each quarter.
What if something happens at 2 AM?
Call the help desk; it is staffed around the clock. The incident plan we wrote together says who isolates what, who is told, and in what order.
Can you just do the assessment?
Yes. A standalone assessment with a prioritised report is a common first step. You can fix the findings with us, with your own people or with someone else.
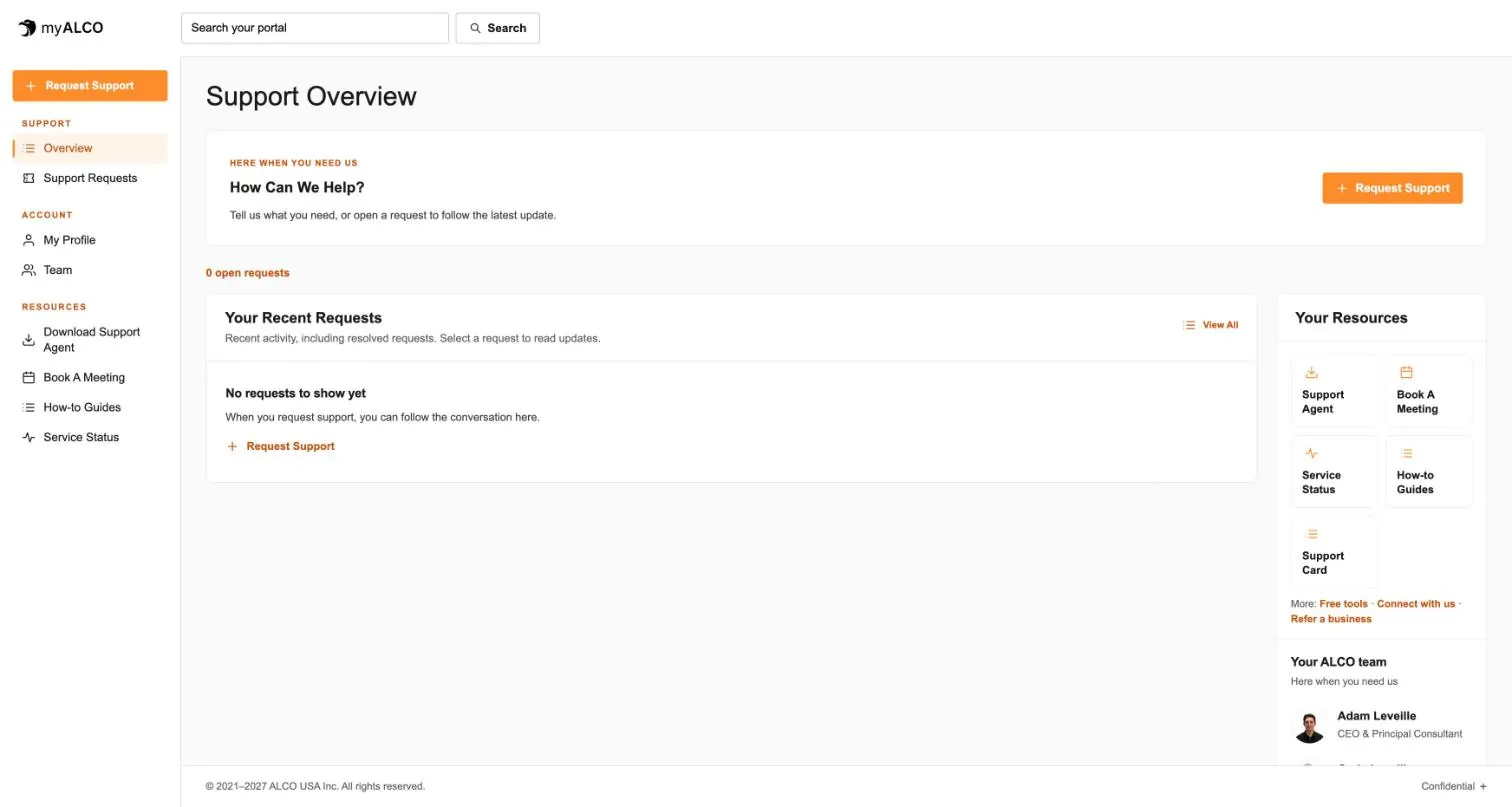
- The client area
Everything ALCO does for you, in one place.
Requests, your team, invoices, documents, shared credentials and sign-in security. One sign-in, any device. Take the tour.
Tour myALCO - New · Our work
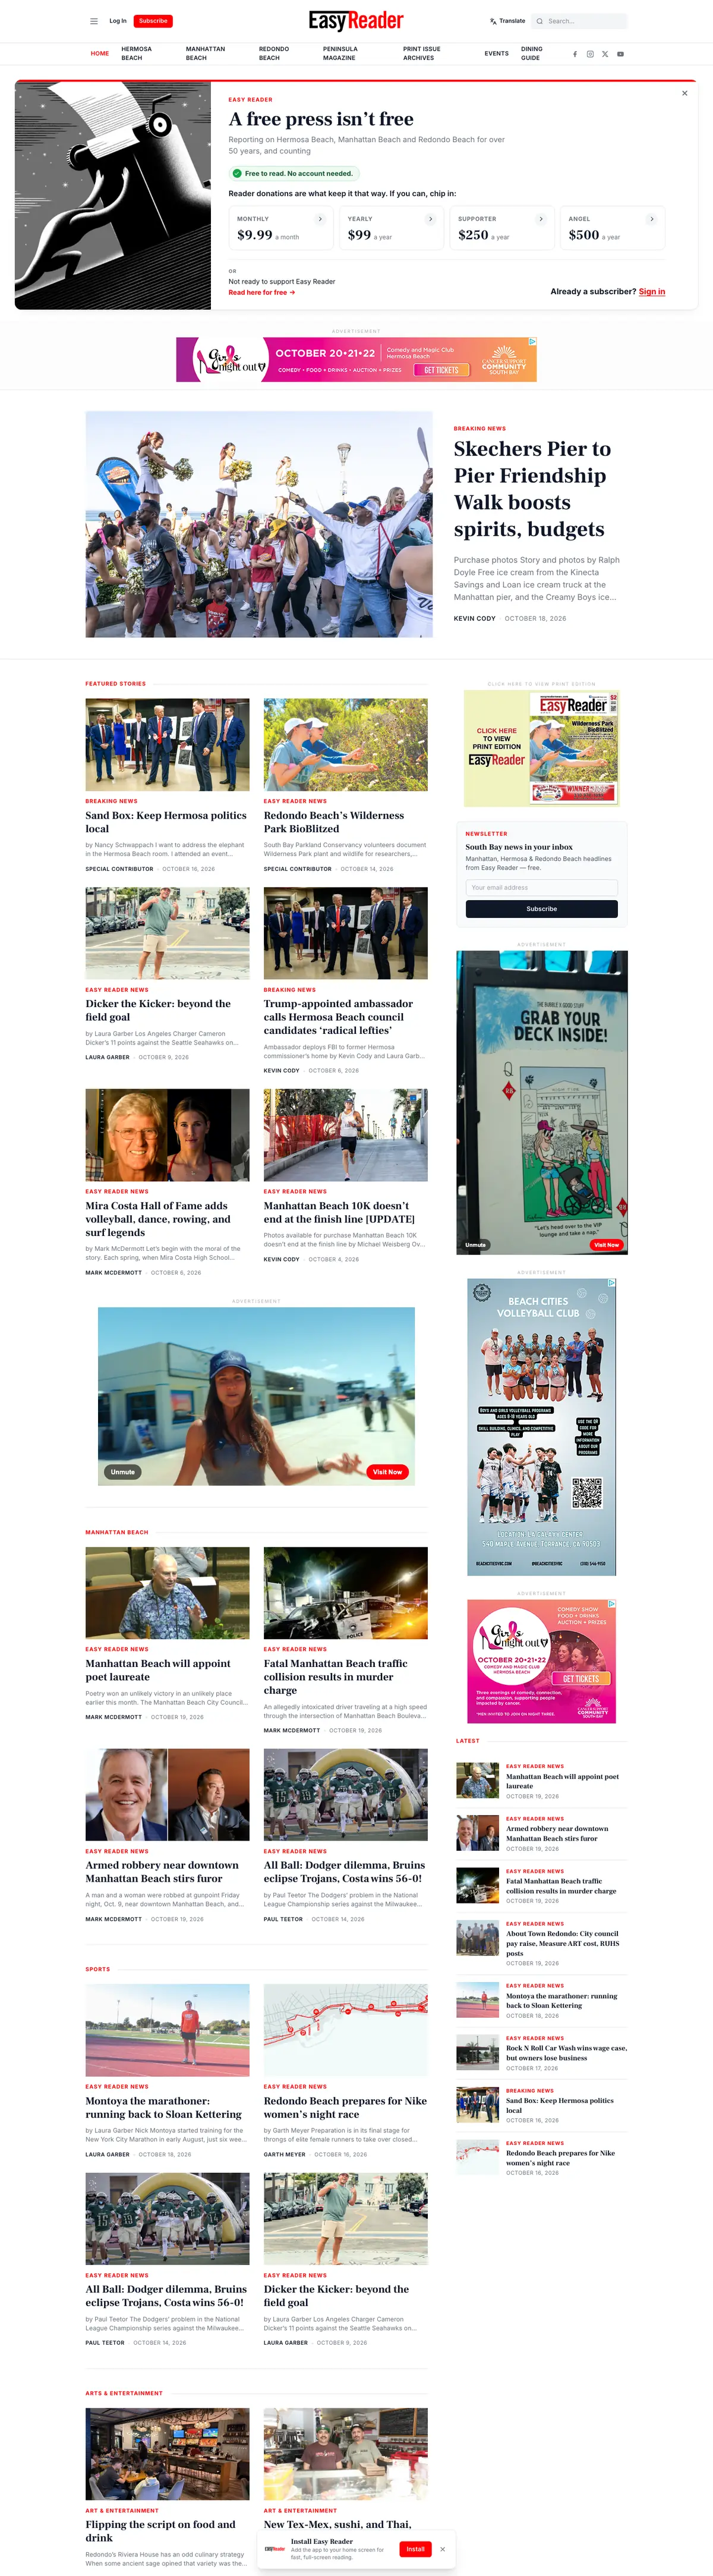
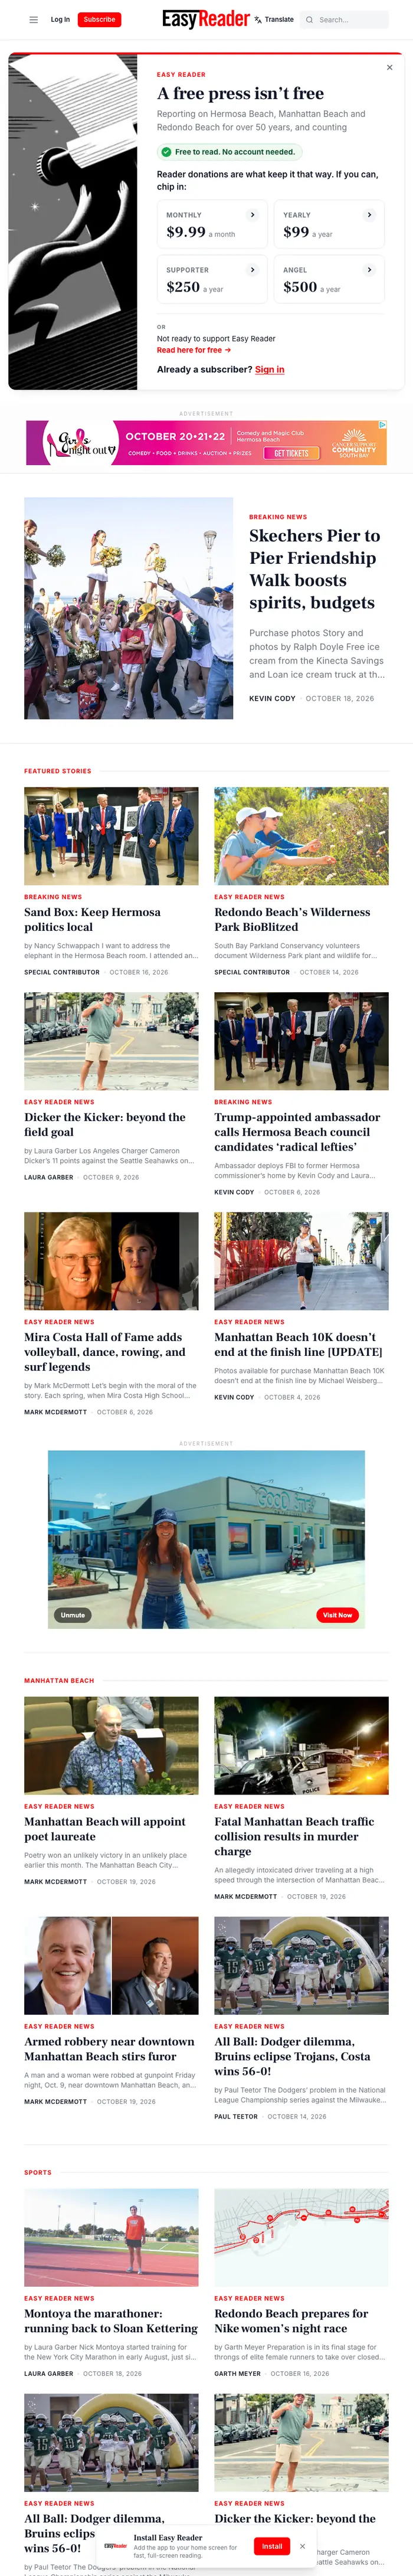
See the sites we have built.
A newspaper rebuilt headless, a parts storefront, two Boise nonprofits and our own site. Every screenshot is the full page, scrolling live.
Browse our work

Clients we’ve worked with
We’ve worked with businesses, nonprofits and community organizations on managed hosting, website development and everyday IT support. These are some of the current and past clients we’ve supported, each with different systems, priorities and people. Explore their stories to see what working with ALCO looks like.